Akira platform version 1.99.22 is available
September 29, 2026
Akira platform version 1.99.22 has been released (tagged at
1.99.22.20260929062732.578d1ce122). This is in a series of releases
made from the 1.99 development branch.
The following are release notes for Akira, Loop, and Dora 1.99.22.
Akira
Nameserver manager reliability
Nameserver status, graphs, and reconfiguration requests made shortly
after a Loop nameserver connects are now handled reliably while the
manager session is still completing its startup handshake. Requests
received during this short bootstrap period are queued until the
connection is ready, avoiding transient Nameserver manager connection
is not ready errors for healthy remote nameservers, including secure
WebSocket connections.
Web interface refinements
The navbar now remains collapsed on screens narrower than larger-screen widths, improving its presentation on tablets and narrower desktop windows.
The page footer has been simplified and its layout
refined. named-manager.conf(5) setup guidance now links directly to
the relevant Loop installation and manager configuration documentation.
UI dependency packages have also been updated as part of routine maintenance.
Loop
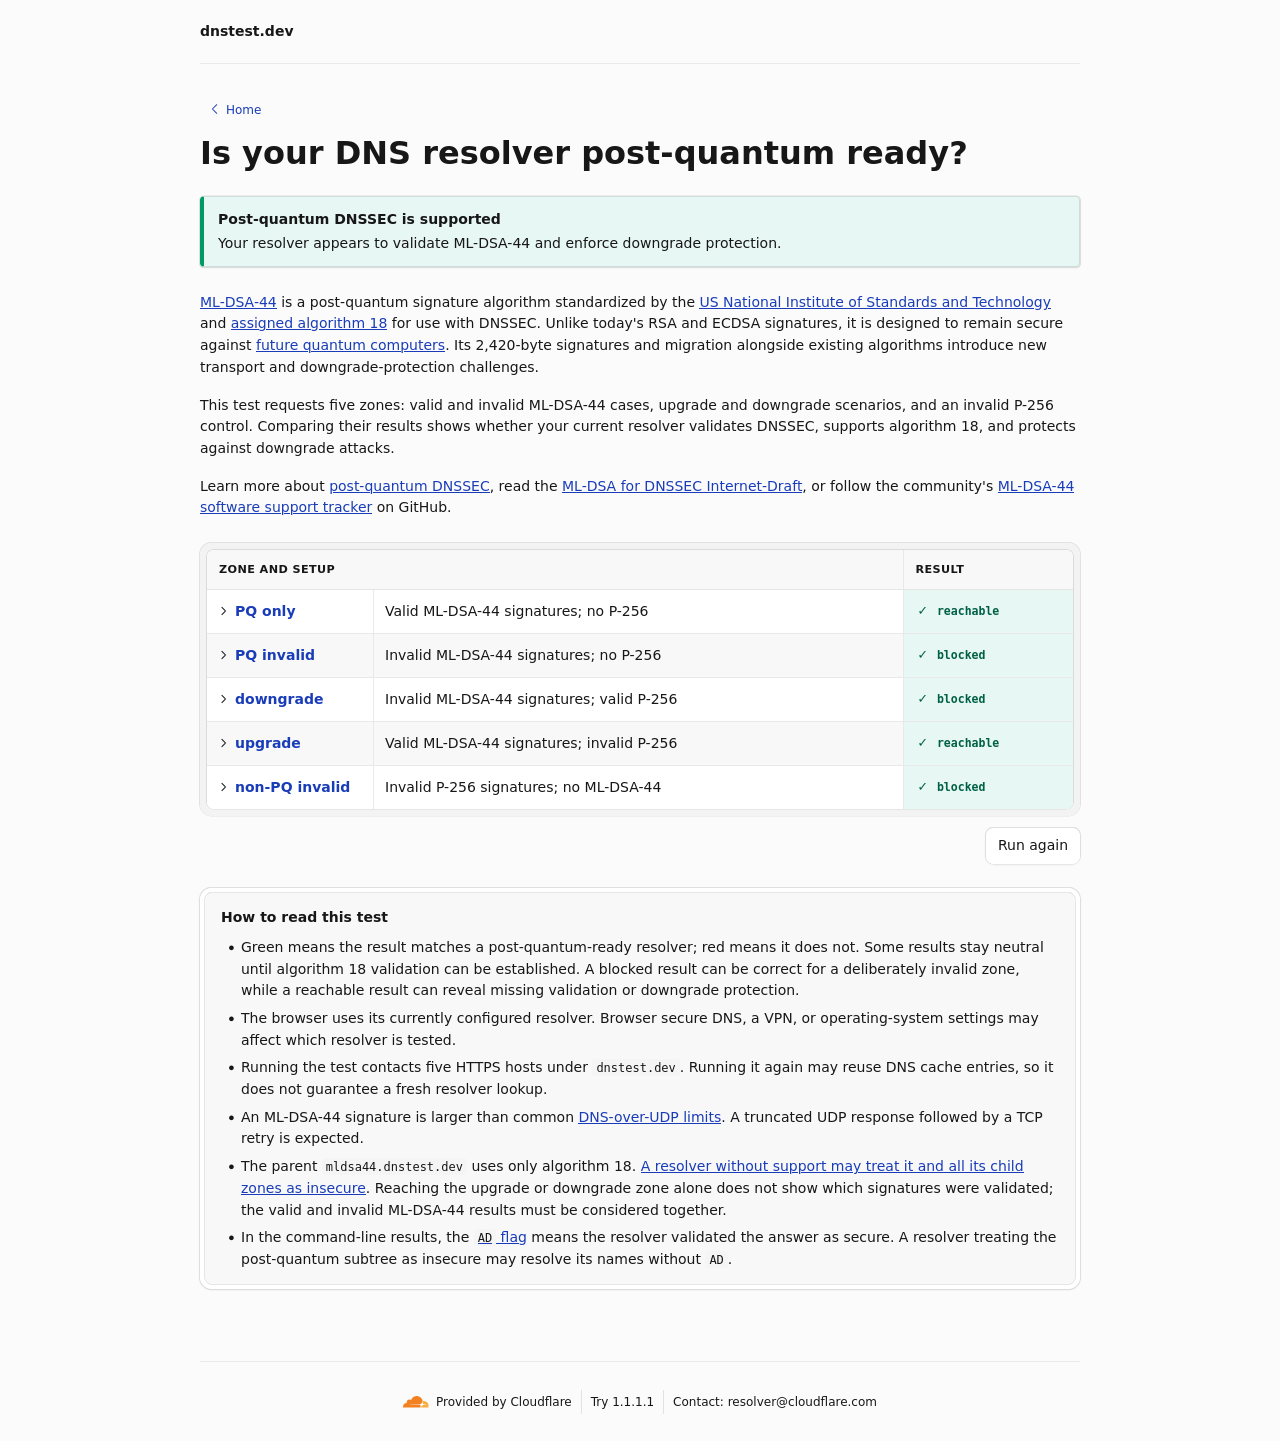
Post-quantum MLDSA44 DNSSEC algorithm support
Loop now supports the quantum-safe MLDSA44(18) DNSSEC algorithm as
specified by draft-westerbaan-dnssec-mldsa-04. Validator and signer
support are fully implemented, and support for validator downgrade
protection as specified in section 7.2 of the draft is enabled by
default. Downgrade protection can be controlled using the new view-level
dnssec-pq-lenient-validation config option in named.conf(5). Support
for encrypted MLDSA44 DNSKEY private keys and PKCS#11 HSM support for
MLDSA44 is also implemented. A screenshot from Cloudflare's
dnstest.dev website testing a Loop resolver follows.
DNSSEC root key rollover
DNSSEC root trust anchor configuration checks recognize the known ICANN root KSK generations and warn when an obsolete 2010 key is still configured, or when a root trust-anchor set is missing keys needed for the current rollover. These checks are limited to actual ICANN root trust-anchor sets so unrelated trust anchors do not generate spurious warnings.
Root key trust anchor sentinel
The resolver restored the DNSSEC root key trust anchor sentinel
mechanism defined by RFC 8509 that had previously been
removed. This allows root-zone operators and resolver operators to
determine whether a validating resolver trusts a particular root KSK
during a rollover. Sentinel processing is enabled by default and can be
controlled with the root-key-sentinel option.
Akira manager reliability
Secure manager connections to Akira now handle commands arriving immediately as the startup configuration handshake completes. This removes a timing race that could otherwise leave a newly connected nameserver unable to service an immediate status, graphs, or reconfiguration request.
Dora
There are no Dora-specific user-visible feature changes in this release.
Changes
Akira
- Queue nameserver manager operations during connection bootstrap so status, graphs, and reconfiguration requests do not fail while a healthy manager session is becoming ready. [RT2401]
- Add direct documentation links to nameserver manager setup guidance. [RT2421]
- Keep the main navigation collapsed until large-screen widths and align the custom collapsed-menu layout with that breakpoint. [RT2420, RT2426]
- Simplify and refine the page footer. [RT2404, RT2415]
- Refresh and correct comments generated in sample data. [RT2416, RT2419]
- Update browser dependency packages. [RT2402]
Loop
- Add support for the quantum-safe MLDSA44 DNSSEC algorithm. [RT2431]
- Add DNSSEC root key trust anchor sentinel support as defined by RFC 8509. [RT2418]
- Add configuration warnings for obsolete or incomplete ICANN root trust-anchor sets. [RT2407, RT2424]
- Avoid root-KSK rollover warnings for unrelated non-root trust anchors. [RT2425]
- Fix a secure manager startup race when commands arrive immediately after the configuration handshake. [RT2401]
Dora
- There are no Dora-specific user-visible feature changes in this release.
Some more development releases will be made from this branch until Akira 2.0 is ready to be branched.