Loop implements a DNS nameserver that can run as an authoritative DNS server, as a caching recursive resolver, or with both functions. It supports DNSSEC, dynamic updates, fine-grained threat-protection policies, live administration, detailed observability, and a complete DNS operations toolset. It can run independently or be managed centrally by Akira. Loop also includes DNSSEC signing and management utilities, DNS diagnostic clients, a dynamic DNS UPDATE client, and performance tools — all the components used to operate DNS services.
Loop is an enterprise-grade DNS nameserver distribution. It is maintained as a DNS reference implementation by closely adhering to the DNS standards. Loop is free for commercial and personal use. It is packaged for Red Hat Enterprise Linux, Fedora, Ubuntu, Debian, Amazon Linux, and Azure Linux.
in one DNS nameserver
Authoritative DNS
Serve primary and secondary zones from RFC 1035 zone master files with efficient replication and durable change tracking.
- Primary and secondary authoritative zones
- DNS NOTIFY, AXFR, and IXFR
- Master files, journaling of changes, and integrity checks
Recursive resolver
Resolve and cache iteratively or through forwarders, selecting upstream servers using measured response times and refreshing hot data before expiry.
- Forwarding, prefetch, and cache controls
- Built-in empty zones and resolver safeguards
- DNSSEC validation
- Smoothed-RTT nameserver selection
- IPv6, DNS64 and dual-stack server controls
Dynamic DNS
Change live authoritative zones with DNS UPDATE while authorization policies and journaling protect and preserve every update.
- RFC 2136 DNS UPDATE support
- Fine-grained update policies
- TSIG authenticated updates
- Kerberos/GSS-TSIG authenticated updates
Live zone lifecycle
Operate a large number of authoritative zones without stopping the server: add or remove zones, refresh replicas, and safely work with dynamic zones.
- Runtime zone add/remove and reconfiguration
- Refresh, retransfer, reload, and NOTIFY controls
- Freeze and thaw zones, journal synchronization
DNS data and transactions
DNSSEC validation and trust
Validate recursive answers against DNSSEC chains of trust and keep trust anchors current without manual updation.
- DNSSEC-validating recursive resolution
- RFC 5011 managed trust anchors
- Static trust anchors
- RSASHA256, RSASHA512, ECDSAP256SHA256, ECDSAP384SHA384, ED25519, ED448, MLDSA44 algorithm support
- Post-quantum downgrade protection
- NSEC and NSEC3 support
- RFC 8509 root trust anchor sentinel checks
Manual & automated zone signing
Sign authoritative zones online and automate the routine work of publishing keys, rolling keys, and maintaining signatures.
- Manual signing with bundled DNSSEC utility programs
- Automatic and inline DNSSEC signing
- Key rollover and periodic re-signing
- RSASHA256, RSASHA512, ECDSAP256SHA256, ECDSAP384SHA384, ED25519, ED448, MLDSA44 algorithm support
- NSEC, NSEC3, OPTOUT, and signing-state controls
Protected DNSSEC keys
Keep private key material encrypted on disk or in PKCS#11 hardware security modules while using the normal DNSSEC workflow.
- Encrypted private-key files at rest
- PKCS#11 HSM key generation and signing
- RSASHA256, RSASHA512, ECDSAP256SHA256, ECDSAP384SHA384, ED25519, ED448, MLDSA44 algorithm support in encrypted private-key files and for HSM key generation and signing
Authenticated DNS transactions
Authenticate updates, transfers, and other DNS transactions using shared-secret, public-key, or Kerberos-based mechanisms.
- TSIG, TKEY, and SIG(0) authentication
- GSS-TSIG/Kerberos authentication
- Key-aware ACLs and update policies
and fine-grained access controls
Views and access control
Present different nameserver configurations and resolver behavior to different clients and tightly scope access to DNS features.
- Split DNS with multiple views
- Address-based and key-based ACLs
- Query, recursion, transfer, and update controls among others
RPZ filtering and abuse resistance
Apply DNS firewall response policies from third-party feeds, and limit reflection and abuse.
- Use up to 64 Response Policy Zones (RPZ) with threat control and filtering policies
- Response Rate Limiting (RRL)
- DNS cookies
Reporting filtering and errors
Return standards-based filtering information and detailed errors when requests are filtered, prohibited due to access control, or fail during processing.
- EDNS Extended DNS Errors
- EDNS Structured DNS Errors
- EDNS options for filtering information
Resolver and resource safeguards
Bound expensive recursive work and memory use with configurable cache, fetch, recursion, TCP, and transfer limits.
- Per-server and per-zone fetch quotas
- Recursion depth, query, and client limits
- Cache size/TTL and transfer resource controls
production DNS operations
Akira-managed operation
Let Akira centrally configure and monitor nameservers over secure authenticated connections while retaining resilient local startup behavior.
- Authenticated management over secure WebSocket that works through corporate firewalls
- Remote configuration management of farms of nameserver groups
- Status monitoring
- Statistics graphs
- Cached configuration and built-in fallback
Statistics and logging
Inspect nameserver, resolver, zone-maintenance, and socket activity with detailed counters, history, and configurable logs.
- XML server statistics
- Statistics recording in time-series RRD databases
- Graph rendering in Akira
- Finely configurable logging system
- Query logging
Administration and hardening
Control a live server remotely and reduce daemon privileges using operating-system isolation and capability controls.
- Remote control using
rndcprogram: reload, cache, zone, and DNSSEC controls - Unprivileged-user and
chroot(2)jail support - Linux capability minimization and resource-limit controls
DNS operator toolset
Query, validate, update, inspect, check, sign, and benchmark DNS using utilities shipped and tested within the same distribution.
diganddelvDNS clients- RFC 2136 DNS UPDATEs using
nsupdate - Configuration, zone, journal, RR, key-generation, and DNSSEC utilities
dnsperfandresperfload testing
Configure, monitor, and manage groups of nameservers centrally with the Akira network manager application.
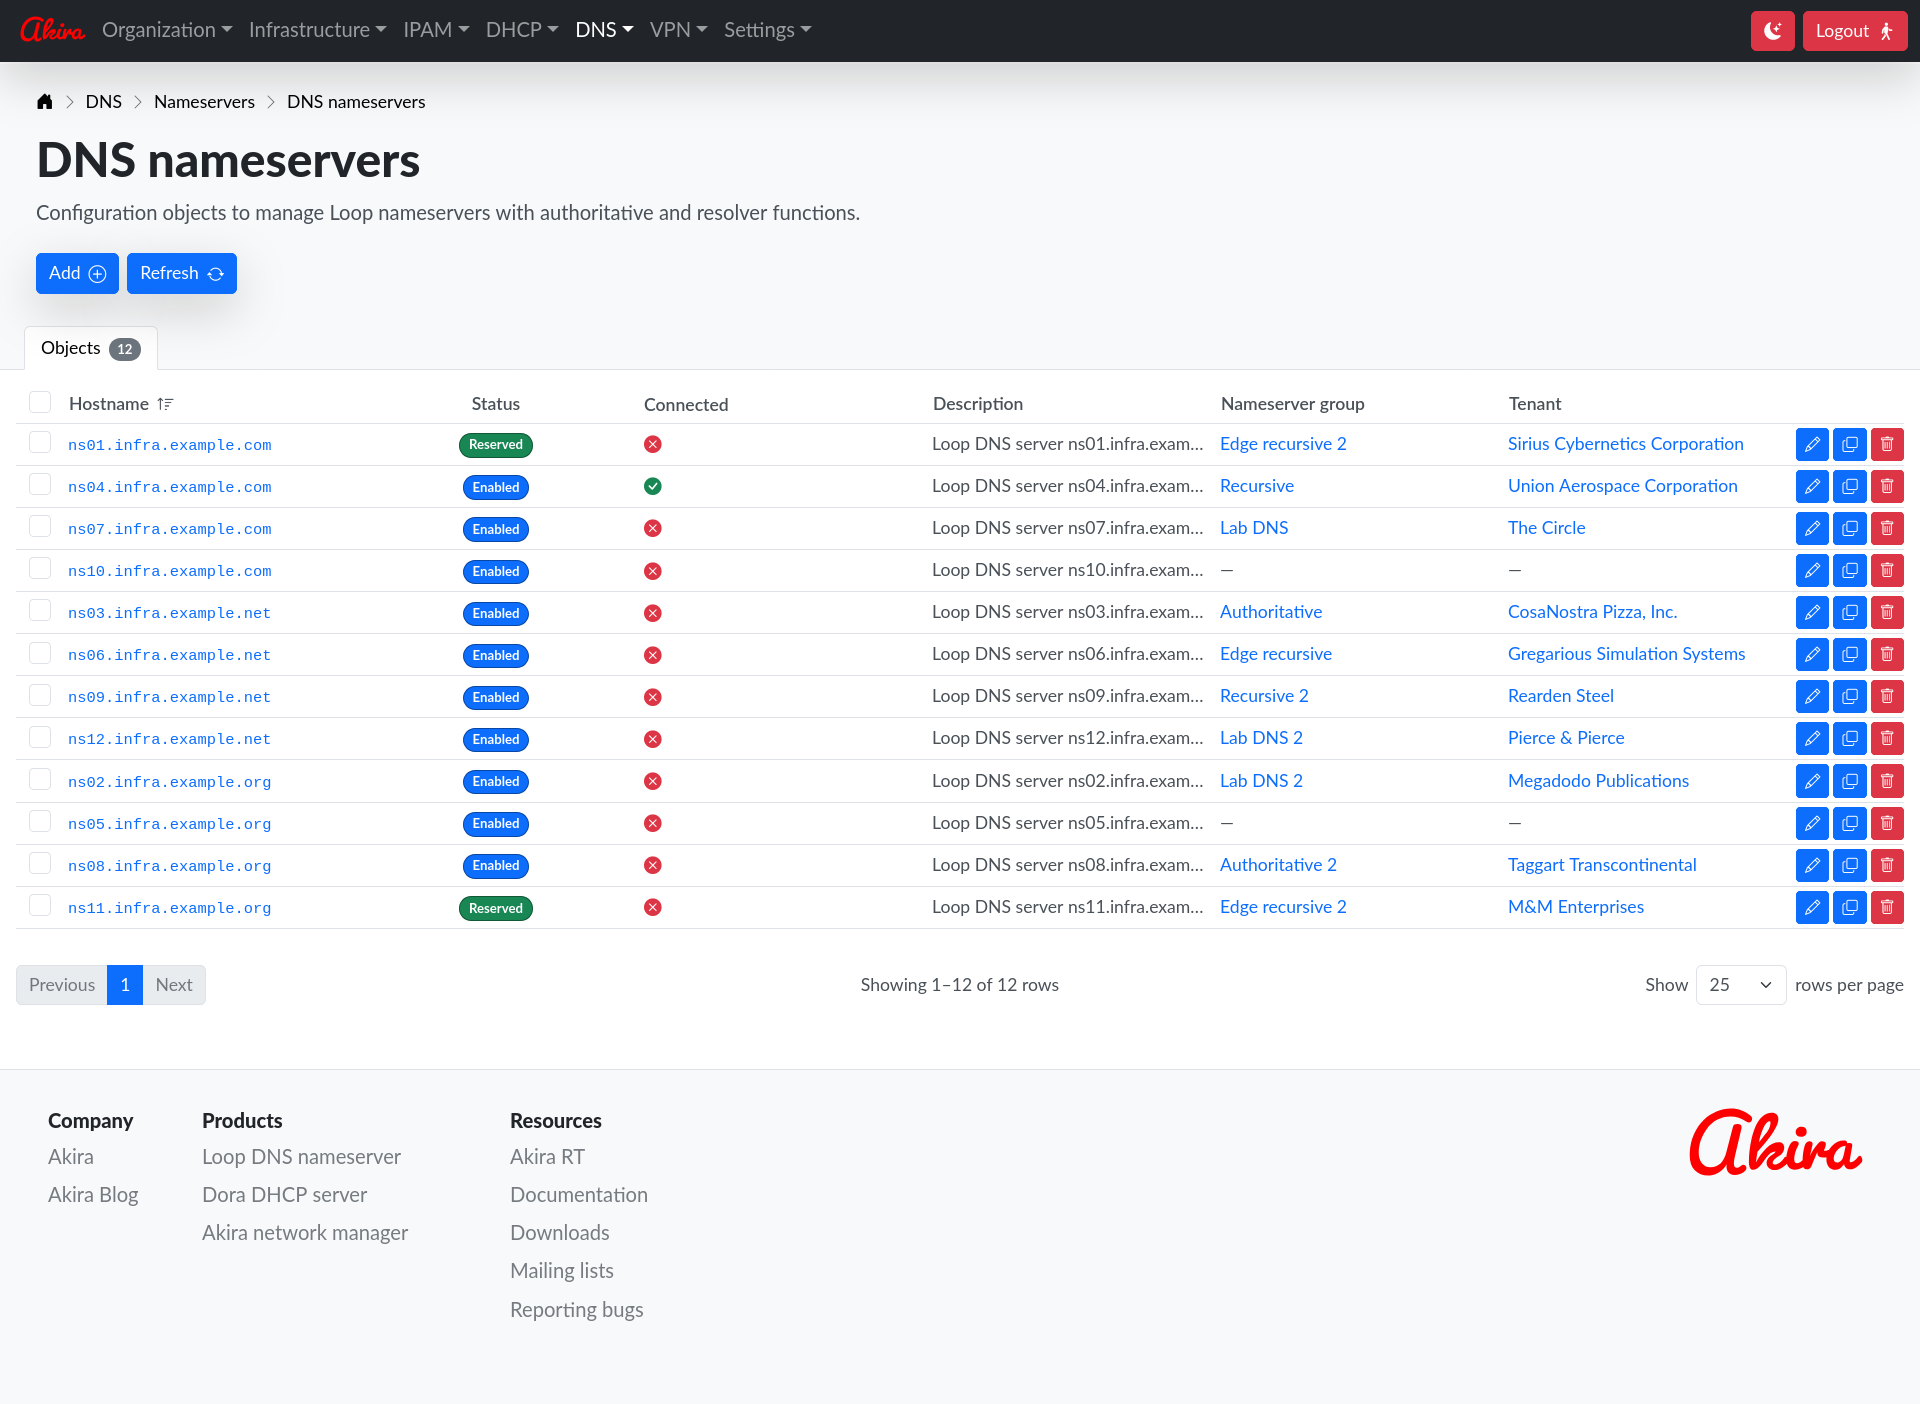
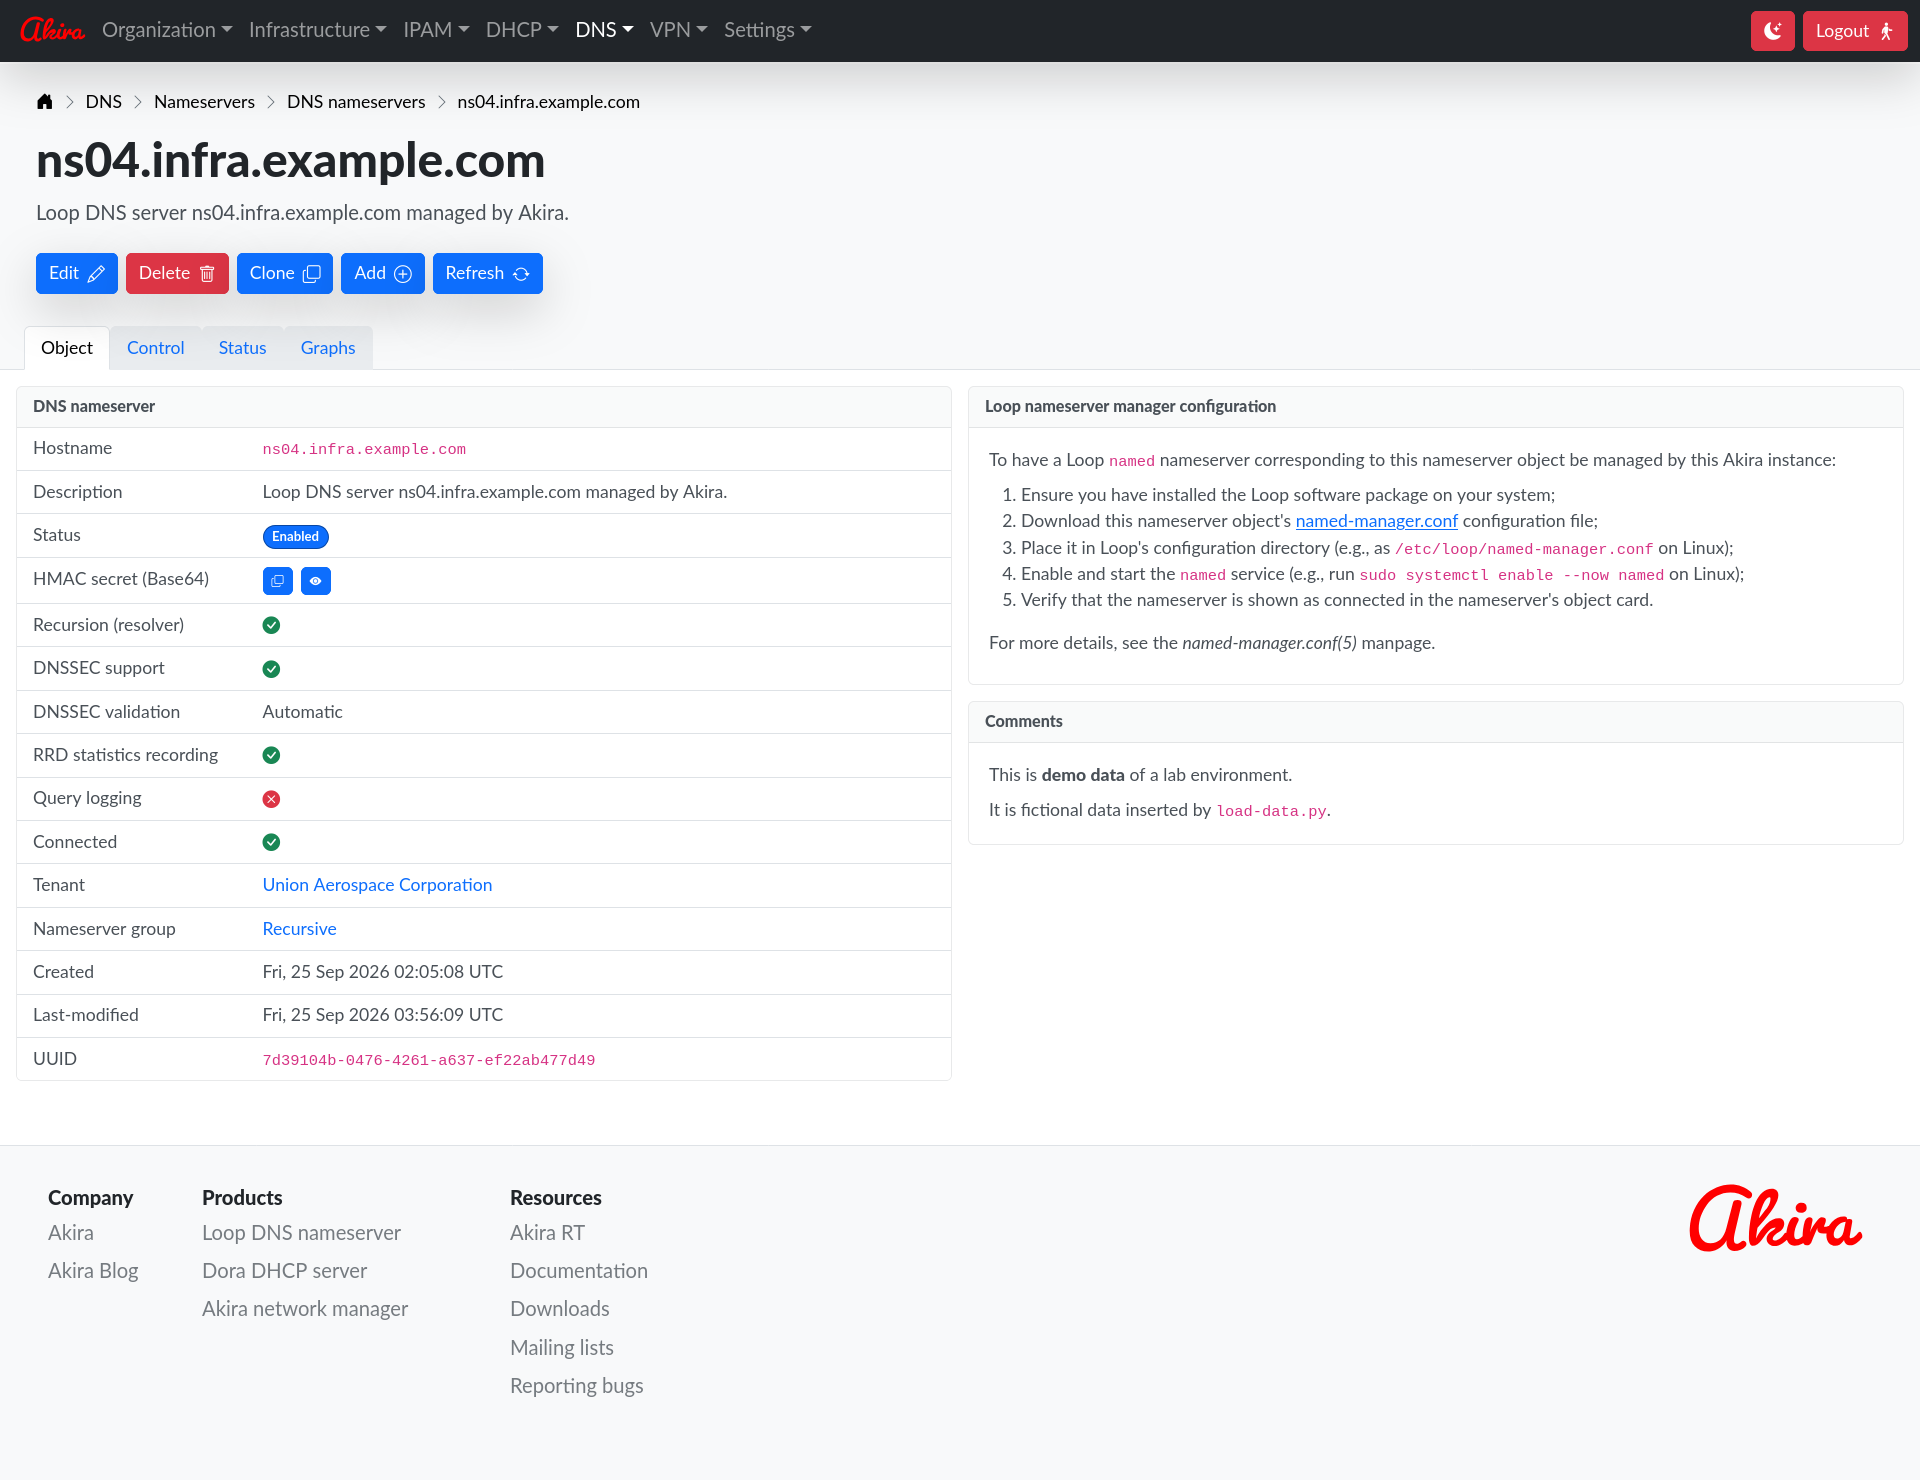
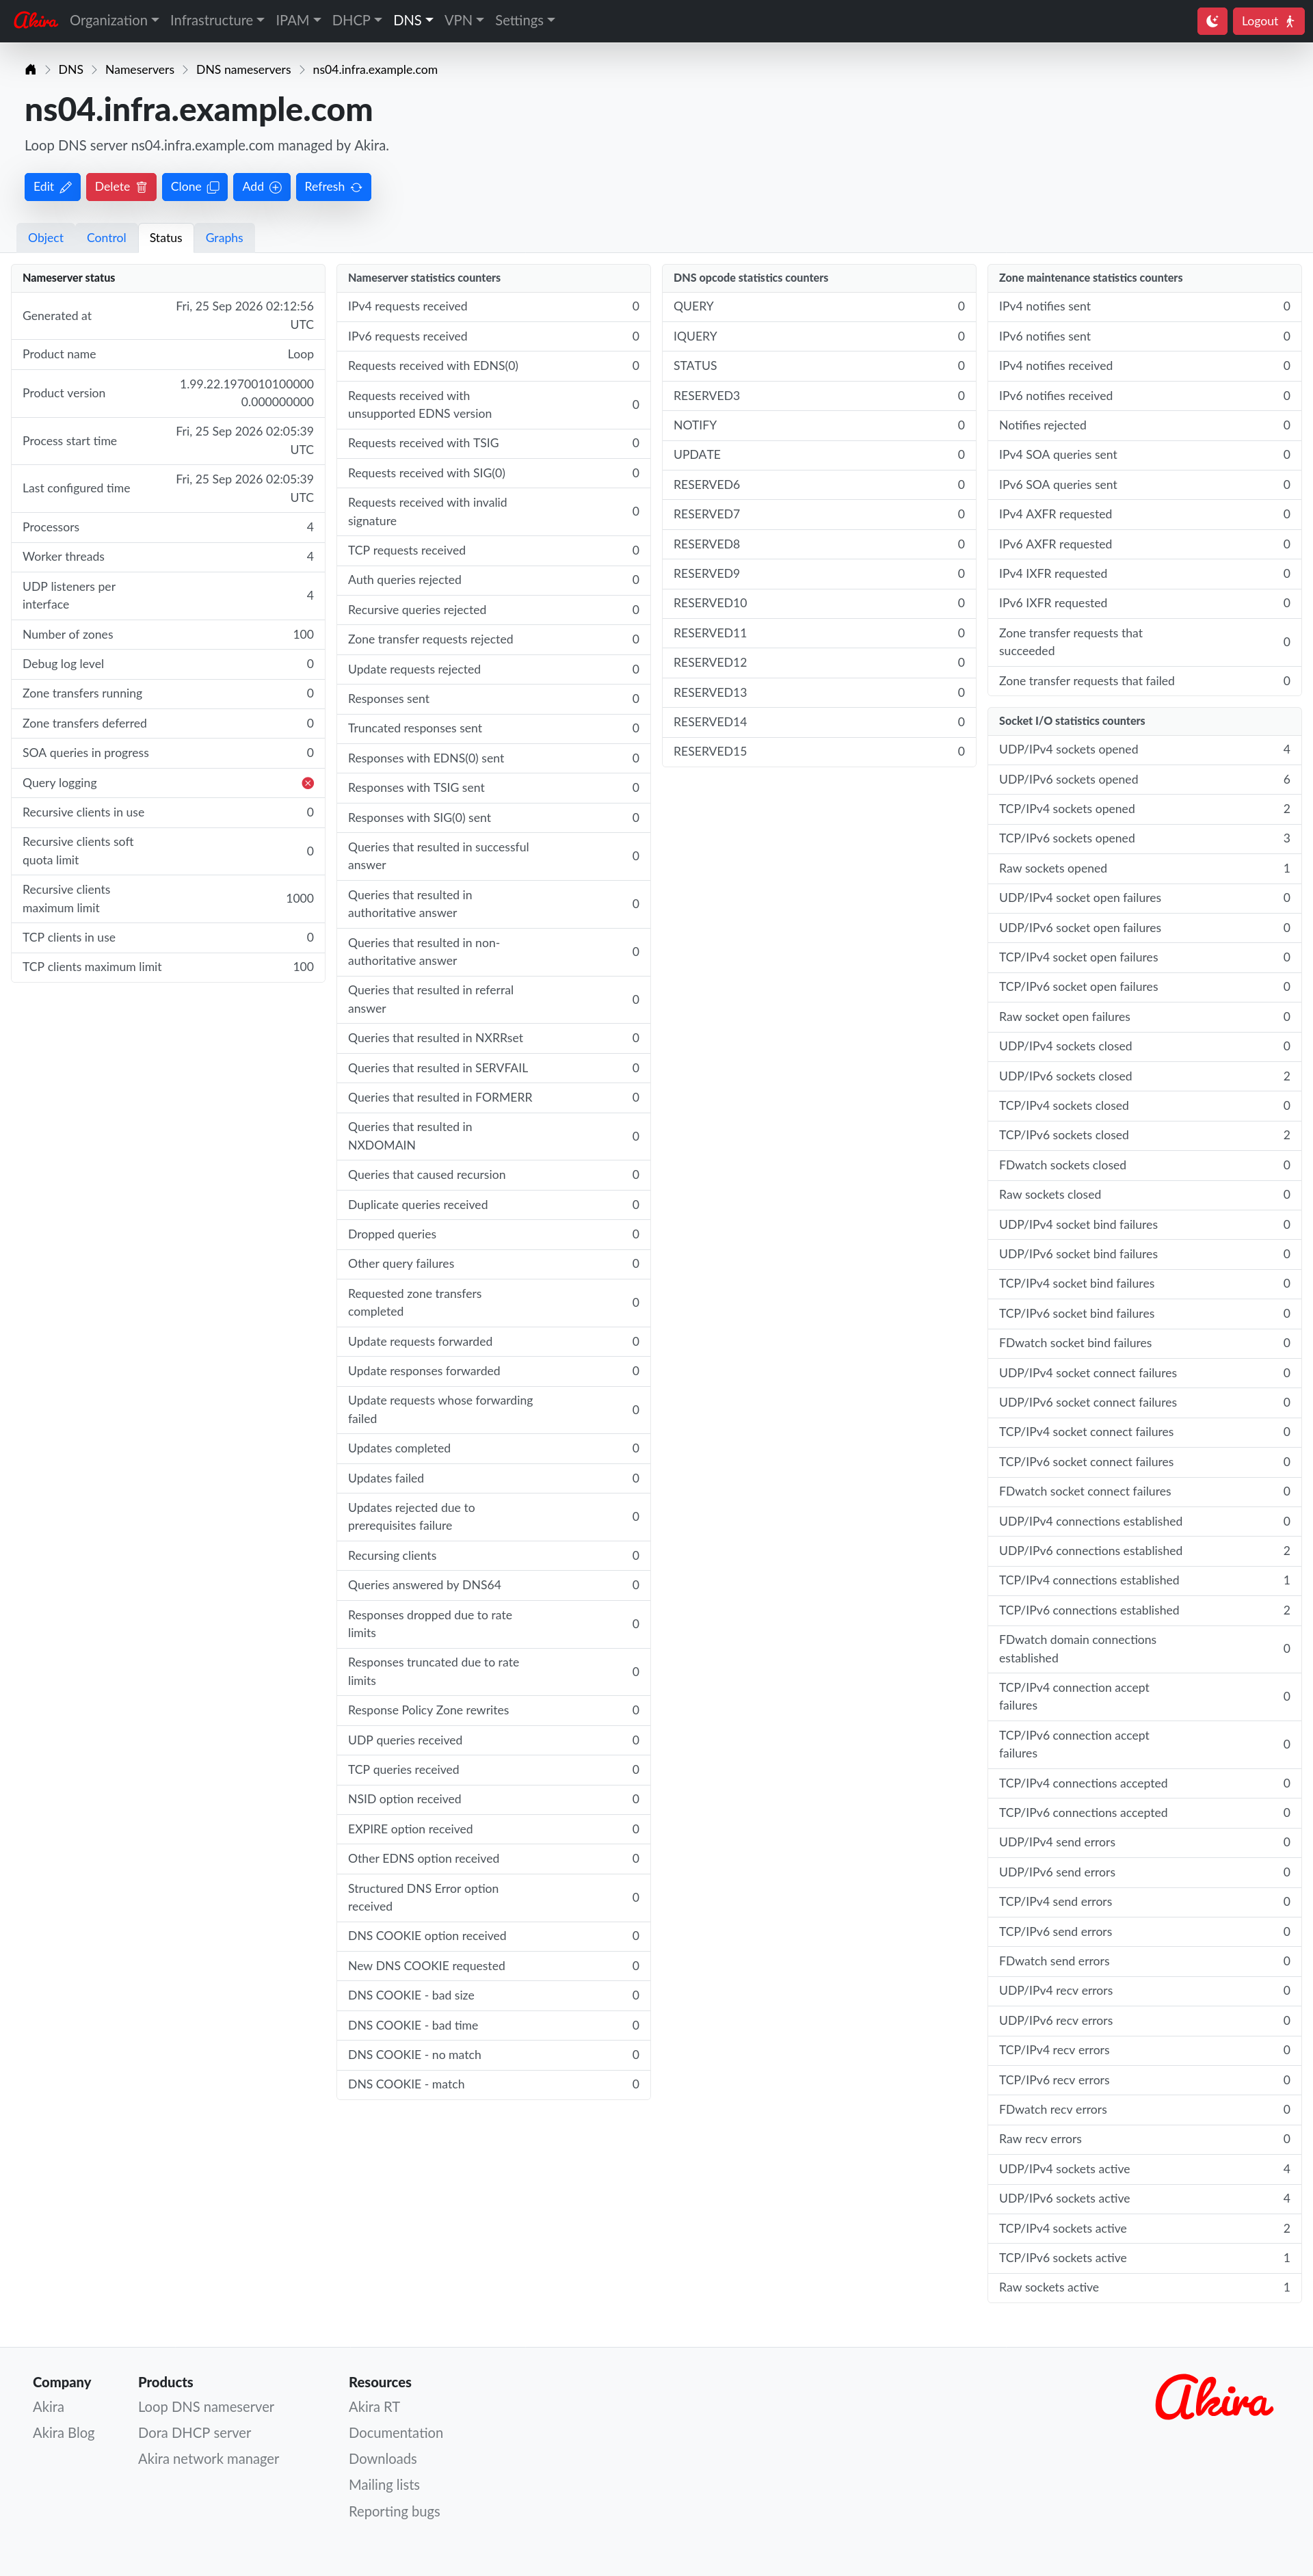
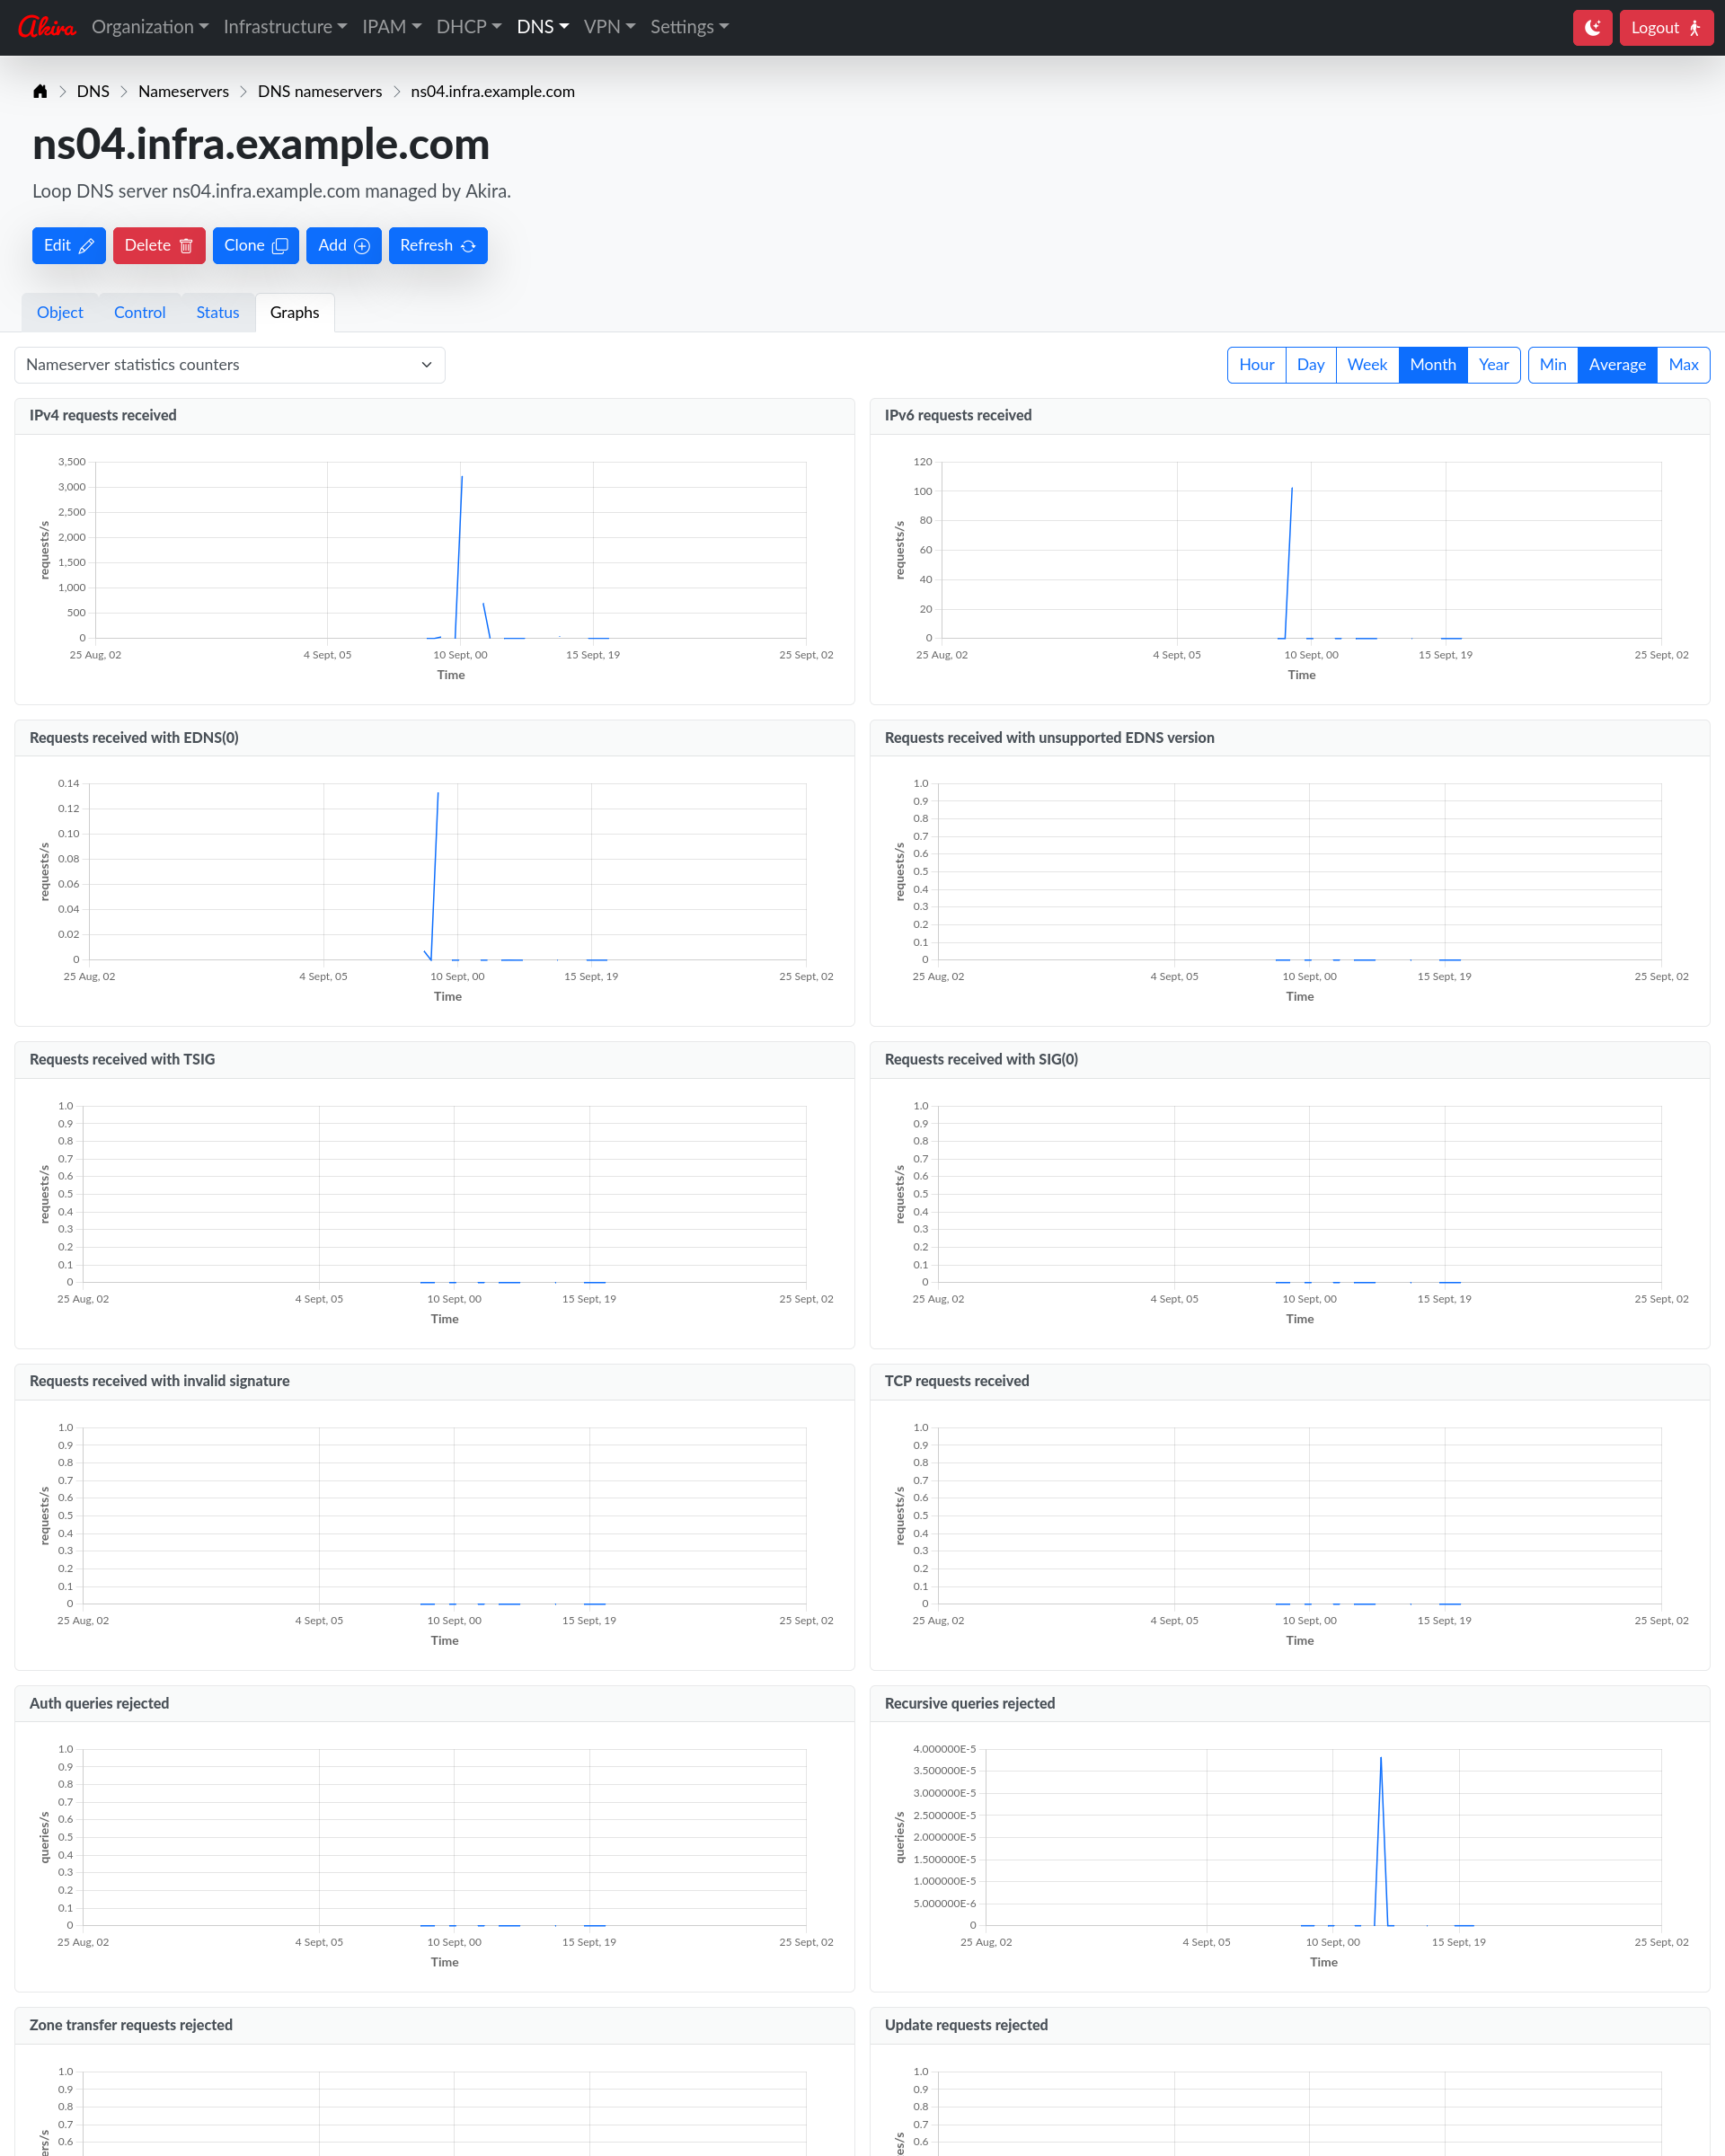
Loop is packaged for Red Hat Enterprise Linux & clones, Fedora, Ubuntu, Debian, Amazon Linux, and Azure Linux.
To install Loop version 1.99.22 on Red Hat Enterprise Linux
10 (x86_64), follow these steps as the root
user.
First, install the akira-release RPM package that will
add the akira-epel
and akira-epel-testing DNF repositories to your system,
as well as associated GPG keys used to verify signed RPM packages from
these repositories:
# dnf install https://download.akira.org/packages/akira/1.99/epel/10/x86_64/akira-release-1.99.22.20260929062732.578d1ce122-1.el10.noarch.rpmThen, install the loop RPM package that will install the
Loop software and documentation:
# dnf install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Red Hat Enterprise Linux
10 (aarch64), follow these steps as the root
user.
First, install the akira-release RPM package that will
add the akira-epel
and akira-epel-testing DNF repositories to your system,
as well as associated GPG keys used to verify signed RPM packages from
these repositories:
# dnf install https://download.akira.org/packages/akira/1.99/epel/10/aarch64/akira-release-1.99.22.20260929062732.578d1ce122-1.el10.noarch.rpmThen, install the loop RPM package that will install the
Loop software and documentation:
# dnf install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Red Hat Enterprise Linux
9 (x86_64), follow these steps as the root
user.
First, install the akira-release RPM package that will
add the akira-epel
and akira-epel-testing DNF repositories to your system,
as well as associated GPG keys used to verify signed RPM packages from
these repositories:
# dnf install https://download.akira.org/packages/akira/1.99/epel/9/x86_64/akira-release-1.99.22.20260929062732.578d1ce122-1.el9.noarch.rpmThen, install the loop RPM package that will install the
Loop software and documentation:
# dnf install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Red Hat Enterprise Linux
9 (aarch64), follow these steps as the root
user.
First, install the akira-release RPM package that will
add the akira-epel
and akira-epel-testing DNF repositories to your system,
as well as associated GPG keys used to verify signed RPM packages from
these repositories:
# dnf install https://download.akira.org/packages/akira/1.99/epel/9/aarch64/akira-release-1.99.22.20260929062732.578d1ce122-1.el9.noarch.rpmThen, install the loop RPM package that will install the
Loop software and documentation:
# dnf install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Fedora Linux
44 (x86_64), follow these steps as the root
user.
First, install the akira-release RPM package that will
add the akira-fedora
and akira-fedora-testing DNF repositories to your system,
as well as associated GPG keys used to verify signed RPM packages from
these repositories:
# dnf install https://download.akira.org/packages/akira/1.99/fedora/44/x86_64/akira-release-1.99.22.20260929062732.578d1ce122-1.fc44.noarch.rpmThen, install the loop RPM package that will install the
Loop software and documentation:
# dnf install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Fedora Linux
44 (aarch64), follow these steps as the root
user.
First, install the akira-release RPM package that will
add the akira-fedora
and akira-fedora-testing DNF repositories to your system,
as well as associated GPG keys used to verify signed RPM packages from
these repositories:
# dnf install https://download.akira.org/packages/akira/1.99/fedora/44/aarch64/akira-release-1.99.22.20260929062732.578d1ce122-1.fc44.noarch.rpmThen, install the loop RPM package that will install the
Loop software and documentation:
# dnf install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Fedora Linux
43 (x86_64), follow these steps as the root
user.
First, install the akira-release RPM package that will
add the akira-fedora
and akira-fedora-testing DNF repositories to your system,
as well as associated GPG keys used to verify signed RPM packages from
these repositories:
# dnf install https://download.akira.org/packages/akira/1.99/fedora/43/x86_64/akira-release-1.99.22.20260929062732.578d1ce122-1.fc43.noarch.rpmThen, install the loop RPM package that will install the
Loop software and documentation:
# dnf install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Fedora Linux
43 (aarch64), follow these steps as the root
user.
First, install the akira-release RPM package that will
add the akira-fedora
and akira-fedora-testing DNF repositories to your system,
as well as associated GPG keys used to verify signed RPM packages from
these repositories:
# dnf install https://download.akira.org/packages/akira/1.99/fedora/43/aarch64/akira-release-1.99.22.20260929062732.578d1ce122-1.fc43.noarch.rpmThen, install the loop RPM package that will install the
Loop software and documentation:
# dnf install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Debian 13 “Trixie”
(amd64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/debian/trixie/amd64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/debian/trixie/amd64/ /" > /etc/apt/sources.list.d/akira-trixie-amd64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Debian 13 “Trixie”
(arm64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/debian/trixie/arm64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/debian/trixie/arm64/ /" > /etc/apt/sources.list.d/akira-trixie-arm64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Debian 13 “Trixie”
(riscv64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/debian/trixie/riscv64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/debian/trixie/riscv64/ /" > /etc/apt/sources.list.d/akira-trixie-riscv64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Debian 12 “Bookworm”
(amd64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/debian/bookworm/amd64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/debian/bookworm/amd64/ /" > /etc/apt/sources.list.d/akira-bookworm-amd64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Debian 12 “Bookworm”
(arm64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/debian/bookworm/arm64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/debian/bookworm/arm64/ /" > /etc/apt/sources.list.d/akira-bookworm-arm64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Ubuntu 26.04 LTS “Resolute Raccoon”
(amd64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/ubuntu/resolute/amd64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/ubuntu/resolute/amd64/ /" > /etc/apt/sources.list.d/akira-resolute-amd64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Ubuntu 26.04 LTS “Resolute Raccoon”
(arm64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/ubuntu/resolute/arm64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/ubuntu/resolute/arm64/ /" > /etc/apt/sources.list.d/akira-resolute-arm64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Ubuntu 26.04 LTS “Resolute Raccoon”
(riscv64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/ubuntu/resolute/riscv64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/ubuntu/resolute/riscv64/ /" > /etc/apt/sources.list.d/akira-resolute-riscv64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Ubuntu 24.04 LTS “Noble Numbat”
(amd64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/ubuntu/noble/amd64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/ubuntu/noble/amd64/ /" > /etc/apt/sources.list.d/akira-noble-amd64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Ubuntu 24.04 LTS “Noble Numbat”
(arm64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/ubuntu/noble/arm64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/ubuntu/noble/arm64/ /" > /etc/apt/sources.list.d/akira-noble-arm64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Ubuntu 24.04 LTS “Noble Numbat”
(riscv64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/ubuntu/noble/riscv64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/ubuntu/noble/riscv64/ /" > /etc/apt/sources.list.d/akira-noble-riscv64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Ubuntu 22.04 LTS “Jammy Jellyfish”
(amd64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/ubuntu/jammy/amd64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/ubuntu/jammy/amd64/ /" > /etc/apt/sources.list.d/akira-jammy-amd64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedTo install Loop version 1.99.22 on Ubuntu 22.04 LTS “Jammy Jellyfish”
(arm64), follow these steps as the root
user.
First, copy the OpenPGP key that apt uses to
verify the release's deb package checksums
into /usr/share/keyrings/:
# curl -o /usr/share/keyrings/akira-archive-keyring.gpg https://download.akira.org/packages/akira/1.99/ubuntu/jammy/arm64/akira-archive-keyring-2026-06-09.gpgThen, add the Akira apt network package
repository for your platform:
# echo "deb [signed-by=/usr/share/keyrings/akira-archive-keyring.gpg] https://download.akira.org/packages/akira/1.99/ubuntu/jammy/arm64/ /" > /etc/apt/sources.list.d/akira-jammy-arm64.listThen, install the loop deb package that will
install the Loop software and documentation:
# apt install loopThen, if you wish to run the nameserver, configure
named suitably by
editing /etc/loop/named.conf, and then run it:
# systemctl enable --now namedNote
Loop is free for commercial and personal use. Please see its license under Loop documentation for more details.
Note
Users of Red Hat Enterprise Linux clones such as Rocky Linux, AlmaLinux, and Oracle Linux can use the Red Hat Enterprise Linux packages of the corresponding version and follow the corresponding installation instructions.
Warning
Amazon Linux and Azure Linux packages are currently alpha releases, i.e., they are published only for testing purposes. They have known outstanding issues due to idiosyncracies of these platforms, which may cause various functions to not work correctly or at all. We will remove this warning when these issues have been resolved.
Note
Raspberry Pi OS users can use the Debian arm64 packages of the corresponding Debian version (e.g., Trixie) and follow the corresponding installation instructions.
Note
On some Linux distributions that have SELinux enabled, you may
notice errors when running the named service such
as:
Aug 10 07:59:06 rpi3 audit[14591]: AVC avc:  denied  { create } for  pid=14591 comm="loop-worker-0" name="tmp-dW3tOeMfdD" scontext=system_u:system_r:named_t:s0 tcontext=system_u:object_r:var_lib_t:s0 tclass=file permissive=0
Aug 10 07:59:06 rpi3 audit[14591]: AVC avc:  denied  { read write open } for  pid=14591 comm="loop-worker-0" path="/var/lib/loop/tmp-dW3tOeMfdD" dev="mmcblk0p3" ino=258270 scontext=system_u:system_r:named_t:s0 tcontext=system_u:object_r:var_lib_t:s0 tclass=file permissive=0
Aug 10 07:59:07 rpi3 audit[14591]: AVC avc:  denied  { rename } for  pid=14591 comm="loop-worker-0" name="tmp-dW3tOeMfdD" dev="mmcblk0p3" ino=258270 scontext=system_u:system_r:named_t:s0 tcontext=system_u:object_r:var_lib_t:s0 tclass=file permissive=0
Aug 10 07:59:07 rpi3 audit[14591]: AVC avc:  denied  { unlink } for  pid=14591 comm="loop-worker-0" name="managed-keys.loop" dev="mmcblk0p3" ino=258227 scontext=system_u:system_r:named_t:s0 tcontext=system_u:object_r:var_lib_t:s0 tclass=file permissive=0
These errors occur because SELinux, when using
the targeted policy, runs the program with
path /usr/sbin/named confined in
the named_t security context. It limits the directories
where the named process can write to. This can be
verified by running the command:
$ ps axZ | grep named
system_u:system_r:named_t:s0    14591 ?        Ssl    0:01 /usr/sbin/named -u loop
The loop package doesn't (and shouldn't)
do anything to solve this issue automatically as it would be a
hack. The SELinux policies for programs such
as /usr/sbin/named are installed by a different package
called selinux-policy-targeted, and are not handled by
the loop package.
You can workaround this issue by either configuring SELinux to run in permissive mode, or by editing the targeted policy to remove the Loop programs from it.
We will rename named in a future release, or have
this issue resolved in the distro packages, upon which this issue
should not occur anymore.
Loop is documented in the Loop User Manual, and manpages are provided for the Loop programs and their config files. The user manual and manpages are also included in the software packages.
| Branch | Type | User Manual | User Manual | Download HTML | README | License |
|---|---|---|---|---|---|---|
| 1.99 | Development | View PDF | View HTML | Download HTML ZIP | View README | View LICENSE.txt |
Paid commercial support is available covering the entire Akira platform of products.
Whatever Akira products you use, you are covered all under one commercial support plan.
Akira platform support plansThree different support options are available. Paid commercial support plans include support for all of Loop, Dora, and Akira together on a per-host basis. |
None
Free
|
Business
US $1,000/month/host
|
Larger operator
US $1,000/month/host
|
| Contract period | Not applicable | None | None |
| Minimum number of hosts | Not applicable | 1 | 64 |
| Support hours | Not applicable | Business hours (9 AM—5 PM) | 24×7 throughout the year |
| Response time | Not applicable | Within 1–2 business days | Immediate ASAP |
| Community discussions on public mailing lists | |||
| Commercial support from Akira by email | |||
| Commercial support from Akira by voice/video | |||
| Access to support tickets system | |||
| Advance information about vulnerabilities |
Paying commercial support customers may follow the instructions provided through their Akira account for receiving support. Other users may use the public Akira mailing lists for community discussions, or email <support@akira.org> for other support requests.